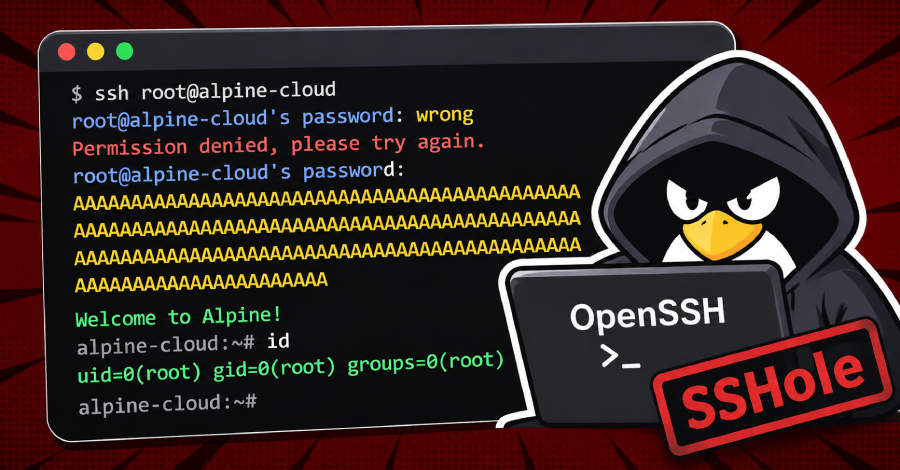
Threat actors are attempting to exploit a recently disclosed OpenSSH flaw, according to Previdian. The vulnerability is tracked as CVE-2026-123158 and carries a CVSS score of 8.1. It is codenamed SSHole (or *sshole).
The flaw can enable sign-ins to accounts that have no password set. According to the report, it impacts Linux systems that run OpenSSH on the musl C library with Pluggable Authentication Modules (PAM) disabled.
The report's headline states that hackers targeted the flaw within hours of disclosure and gained root on a honeypot. The supplied excerpt ends before giving further detail on that claim, so the report does not confirm the scope of the activity beyond the attempts Previdian describes.