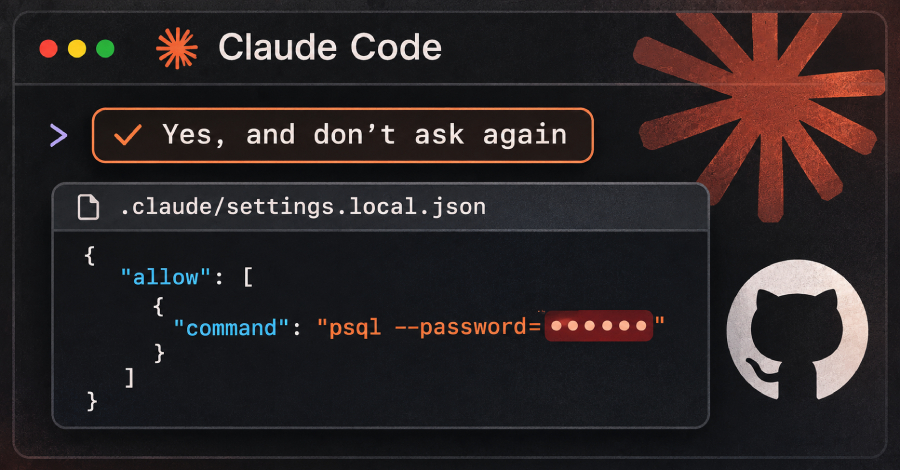
Passwords and API keys typed into commands that developers approved in Claude Code are appearing in public GitHub repositories. The source report says that when a user selects "Yes, and don't ask again," Anthropic's AI coding assistant can save the command word-for-word, including the secret, in a project settings file.
Software security company Apiiro said 1,122 public copies of such files contain exposed credentials, according to the report. The report is cut off after that figure, so it does not say what kinds of credentials were found, which services they belong to, or whether any have been used.
The source does not describe Anthropic's response or any fix.