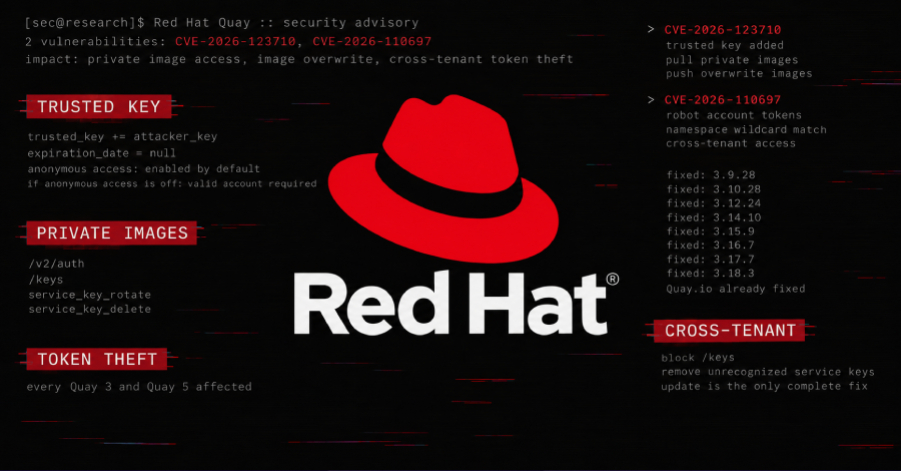
A critical flaw in Red Hat Quay lets an attacker who can reach a Quay registry read and overwrite private container images in every repository, according to the report.
Quay allows anonymous access by default. While anonymous access is enabled, the attacker needs no account to exploit the flaw. Red Hat said that if anonymous access is turned off, anyone with a valid account can still exploit it.
Red Hat has released fixed builds for eight Quay versions, the report says.