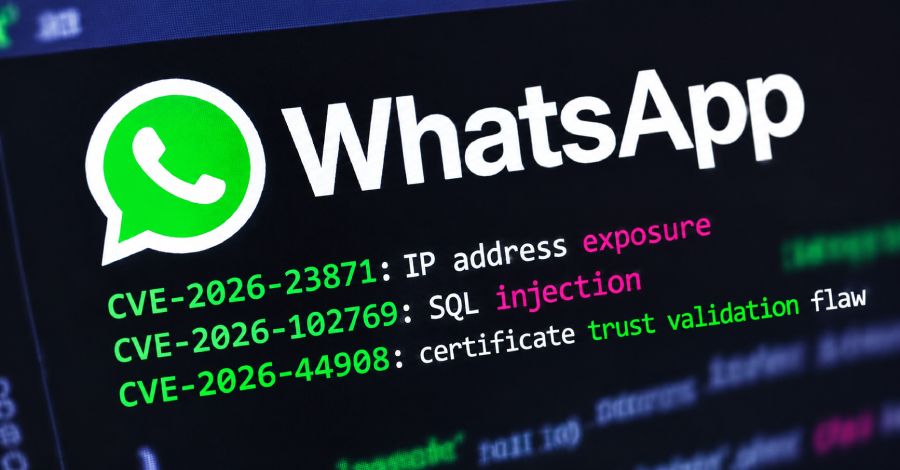
WhatsApp patched three security flaws, according to the report. Meta-owned WhatsApp fixed one bug in its Android app that the company suspects may have been exploited in connection with scam messages.
The Android vulnerability is tracked as CVE-2026-23871. The report describes it as incomplete validation of external ad-reply URLs in WhatsApp for Android and WhatsApp Business for Android before version 2.26.17.4.
The report cuts off before describing what the flaw could allow, so the impact is not stated in the source.