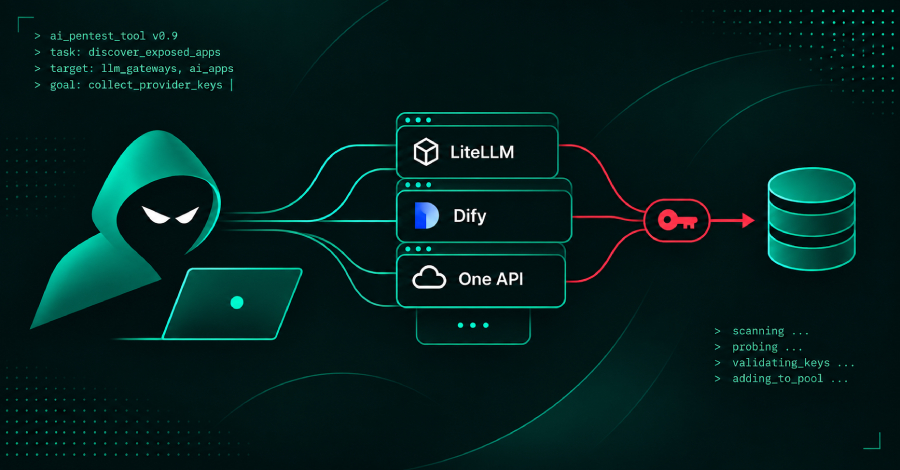
Amazon's threat intelligence team reported an AI agent campaign that targets internet-exposed AI applications, including LiteLLM, One API, and Dify. According to the report, attackers' AI agents search for weak spots in these apps to steal the AI provider keys stored inside.
Amazon's team captured the agents' own records using decoy servers. The records describe stolen keys being used to run the AI models that powered the search for more keys.
The source excerpt ends before giving further details, so the report does not confirm the scope of affected systems or the number of compromised keys.