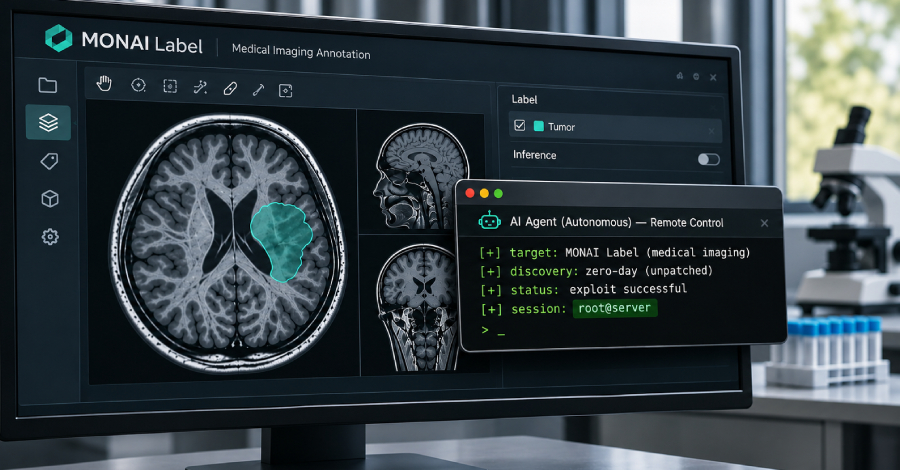
Suspected China-linked hackers used autonomous AI agents to find a previously unknown flaw in MONAI Label, an open-source medical imaging server, according to Amazon Threat Intelligence. Amazon said the hackers used the flaw to gain root access to a university server.
The flaw lets an attacker with no account write files outside the server's storage folder. Amazon said it affects MONAI Label 0.8.5 and earlier in the default setup.